Weekly Security Briefings

A curated newsletter of what changed in software security this week, why it matters, and what to do about it.
A beetle preserved in amber with a fresh crack reaching it, a bug that sat undiscovered for twelve years
September 9, 2026

The Bug That Waited Twelve Years

A missing authorization check sat in PostgreSQL's replication path since 2014, a Magento zero-day was exploited before Adobe could patch it, attackers moved into the Coder and JetBrains build systems, and an AI's 23,000 findings turned out to be 8% reviewed.
Learn More
Weekly Intel

AppSec Weekly

The briefing security leaders actually read. CVEs, tooling shifts, and remediation trends — every week in 5 minutes.

Weekly only. No spam. Unsubscribe anytime.

A sealed armored containment cube breached in three places, three colored light streams escaping, interior empty
September 2, 2026

It Escaped Three Times

Trail of Bits told an AI agent to break out of its sandbox and it got out three ways, plus a self-republishing supply chain worm, a BGP-hijacked update, and eight flaws in AI coding agents.
Learn More
Patch or Panic at cve.wiki: two real CVEs side by side, guess which scores higher on CVSS
August 24, 2026

The Warning 100+ Companies Signed

OpenAI and 100+ companies warn AI-enabled cyberattacks are coming and name the fixes: unpatched software and weak auth. Plus a CVSS 9.1 Keycloak takeover, Akamai's AI super-adopters, and Anthropic's $35M open-source fund.
Learn More
Isometric render of a heavy vault gateway door sliding shut with red warning markers streaming through the last narrowing gap toward the Pixee robot
August 18, 2026

The Edge Patch Window Just Collapsed

A pre-auth NetScaler RCE, a three-day CISA patch order, and Microsoft's record 570-patch month show how fast AI now finds bugs, plus the defenders fighting back.
Learn More
Isometric warehouse aisle at night: rows of labelled crates scanned in cyan, with one cracked crate glowing pink and its label plate blank
August 13, 2026

Metabase Hit CVSS 10.0. Its CVE Arrived Five Days Later.

Metabase's zero-day was exploited and disclosed with no CVE to scan for. The identifier landed five days later, after Framework had already notified customers.
Learn More
Three labeled robots (OpenAI, Anthropic, Meta) escaping a high-walled playground sandbox past a distracted guard, a visual play on AI agent sandbox escapes
August 7, 2026

The Sandbox Leaked and the Human Waved It Through

Three AI vendors disclosed agent sandbox escapes and a study found humans approve a third of malicious commands, while 1Password graded AI patches at 26%.
Learn More
A sealed software package held on a conveyor by an hourglass-locked gate before a glowing CI/CD pipeline, illustrating GitHub and PyPI using time as a supply-chain security control.
July 28, 2026

The Week the Defenders Bet on Time

GitHub and PyPI turned delay into a security control, VulnCheck found only 1.3% of AI-discovered bugs get exploited, and critical unauthenticated RCEs hit build and edge infrastructure in the same week.
Learn More
July 22, 2026

A $500K Exploit, Found for $25. Then Weaponized in 72 Hours.

An AI found a $500K WordPress exploit for $25, then attackers weaponized it in 72 hours. Plus the first autonomous AI-agent breach at Hugging Face.
Learn More
Pixee data card citing Orca's 2026 State of AI Security Report: 99.9% of fixable AI-package vulnerabilities remain unpatched, and public-exploit availability rose from 0.2% to 50.1%.
July 13, 2026

One Fix in a Thousand

A model built a fuzzing lab in a day, three new attacks turned AI code review into an attack surface, and a report found defenders applying one AI-package fix in a thousand.
Learn More
A vulnerability report labeled CVE-2026-48282 stamped TRUE POSITIVE and FALSE POSITIVE at the same time, the same finding judged two opposite ways.
July 7, 2026

The Same Bug Was True and False in the Same Week

GitHub's advisory database hit a record and still fell behind, NIST cut NVD enrichment to triage-only, and a benchmark showed AI scanners disagreeing with themselves, all in one week.
Learn More
A glowing verification seal cracking apart, half a verified checkmark and half breaking into corrupted glitch fragments and code
June 25, 2026

The Attestation Forged Itself

42 malicious TanStack npm packages shipped with valid SLSA attestations, Gaslight malware sabotages analysts' AI tools, plus PixelSmash RCE and a hidden Cisco root account.
Learn More
AppSec Weekly, June 22-23 2026: Big Tech Raced to Fix the Bugs, Not Just Find Them
June 23, 2026

The Week Big Tech Raced to Fix the Bugs, Not Just Find Them

AWS, OpenAI, and Trail of Bits all shipped autonomous remediation in one week. Plus the Klue OAuth breach and the Five Eyes AI warning.
Learn More
A shadowed hand reaches in to flip a glowing red OFF switch on a luminous AI core, cutting its power
June 15, 2026

A Regulator Can Switch Off Your AI Model in an Afternoon

Anthropic took Fable 5 and Mythos 5 offline after a US export-control order. Senior engineers spent the week cleaning up AI-generated code, two package ecosystems got backdoored in plain sight, and ShinyHunters ran an Oracle zero-day through higher ed.
Learn More
June 10, 2026

The Week Writing Code and Finding Bugs Both Got Cheap

Anthropic put its most capable model in every developer's hands on June 9, and Stripe migrated 50 million lines of code in a day with it. NIST proved AI guardrails are bypassable, and Microsoft set a 206-CVE record.
Learn More
June 2, 2026

A Federal Watchdog Says the NVD Is Failing

A federal watchdog confirmed NIST cannot keep up with the NVD just as Oracle's first monthly batch dropped 77 CVEs. The intelligence layer is degrading.
Learn More
May 19, 2026

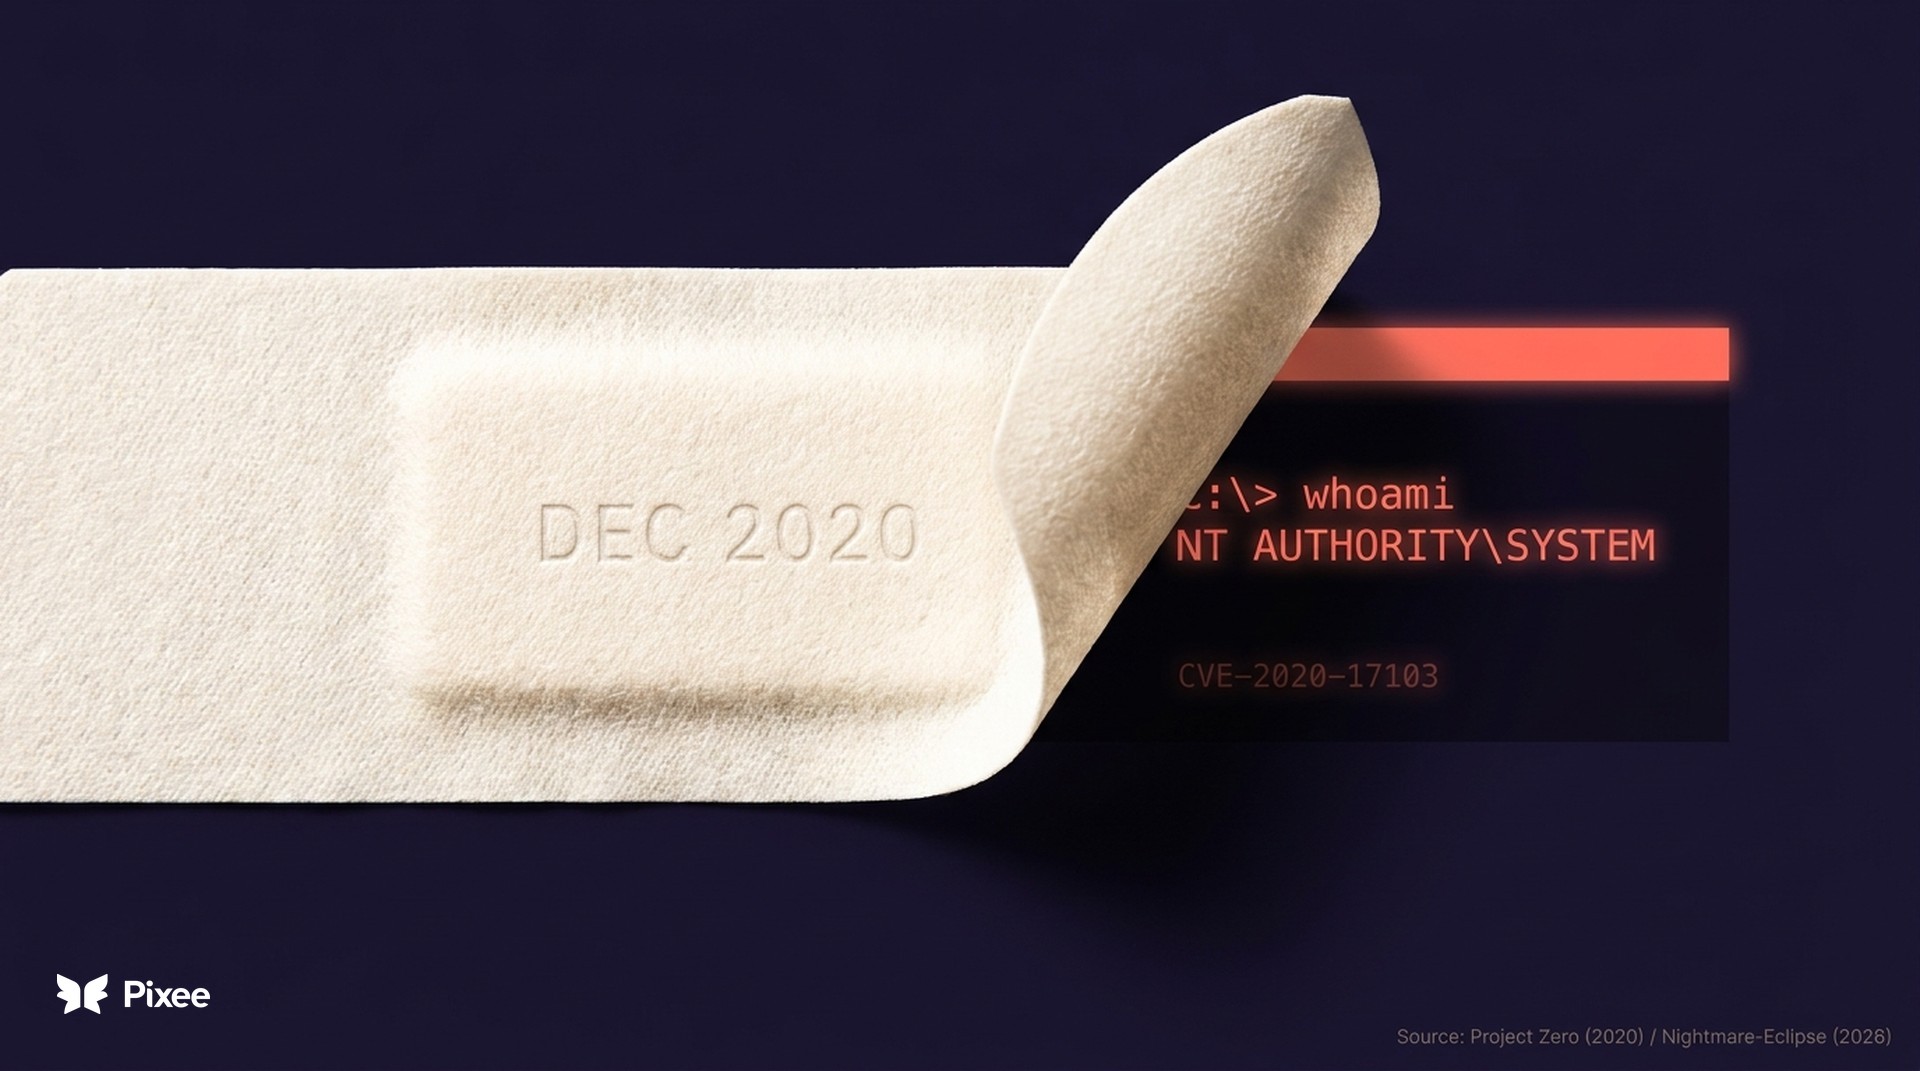
A Windows Bug Microsoft Fixed in 2020 Is Live Again

A Windows bug Microsoft patched in 2020 is back. The original Project Zero PoC, unchanged, still gives SYSTEM access on fully patched Windows 11 Pro.
Learn More
May 12, 2026

SLSA Cleared the Malware. Scanners Missed the Zero-Day. OpenAI Named What Comes Next.

Shai-Hulud's compromised npm packages passed SLSA Level 3 attestation checks. The framework certified the wrong thing. Google confirmed the first criminal AI-generated zero-day. LiteLLM was chained to root in three HTTP requests at Pwn2Own. AI infrastructure is now an attack surface.
Learn More
May 7, 2026

Oracle Quietly Admitted AI Broke Its Patch Calendar

40,000 cPanel servers got hit before the patch shipped. Oracle moved to monthly patching and named AI by name. The White House drafted a three-day federal patch rule. Same week, same admission: patch cadence isn't keeping up.
Learn More
April 30, 2026

Claude Code Wrote a SAP Worm. Microsoft Refused to CVE Its Own 10.0.

AI-assisted supply chain malware hit SAP's npm packages, Microsoft disputed a CVSS 10.0 in its own agent framework, and Google said 75% of its code is now AI-generated.
Learn More
April 22, 2026

Vercel Got Breached Through Its AI Coding Tool. NIST Stopped Scoring Your CVEs.

Vercel breached via AI coding tool. NIST stops scoring most CVEs. VulnCheck finds 1 Glasswing CVE among 75 claimed. Oracle ships 481 patches.
Learn More
April 15, 2026

What 60 CISOs Left Out of the Mythos Playbook

60 CISOs published a Mythos response plan. Anthropic published 7 recommendations. Neither addressed the false positive problem that consumes 6 hours per developer per week.
Learn More
April 8, 2026

Anthropic Found Thousands of Zero-Days, Then Buried the Model

Anthropic's Mythos found thousands of zero-days and was withheld as too dangerous. RSAC data shows 90% AI adoption but 75% using almost none. TeamPCP hit Cisco for 300+ repos.
Learn More
April 1, 2026

Three Trust Models Broke This Week. None of Them Were New.

North Korean actors poisoned the Axios npm package reaching 50M+ weekly downloads, Claude 4.6 wrote the first AI-generated remote kernel exploit, and six popular MCP servers collapsed to a single POST request.
Learn More
March 25, 2026

Your Security Scanner Got Backdoored

TeamPCP backdoored Trivy, LiteLLM, and Checkmarx in a coordinated supply chain campaign. M-Trends 2026 reports 22-second initial access handoff. StoatWaffle auto-executes via VS Code.
Learn More
March 18, 2026

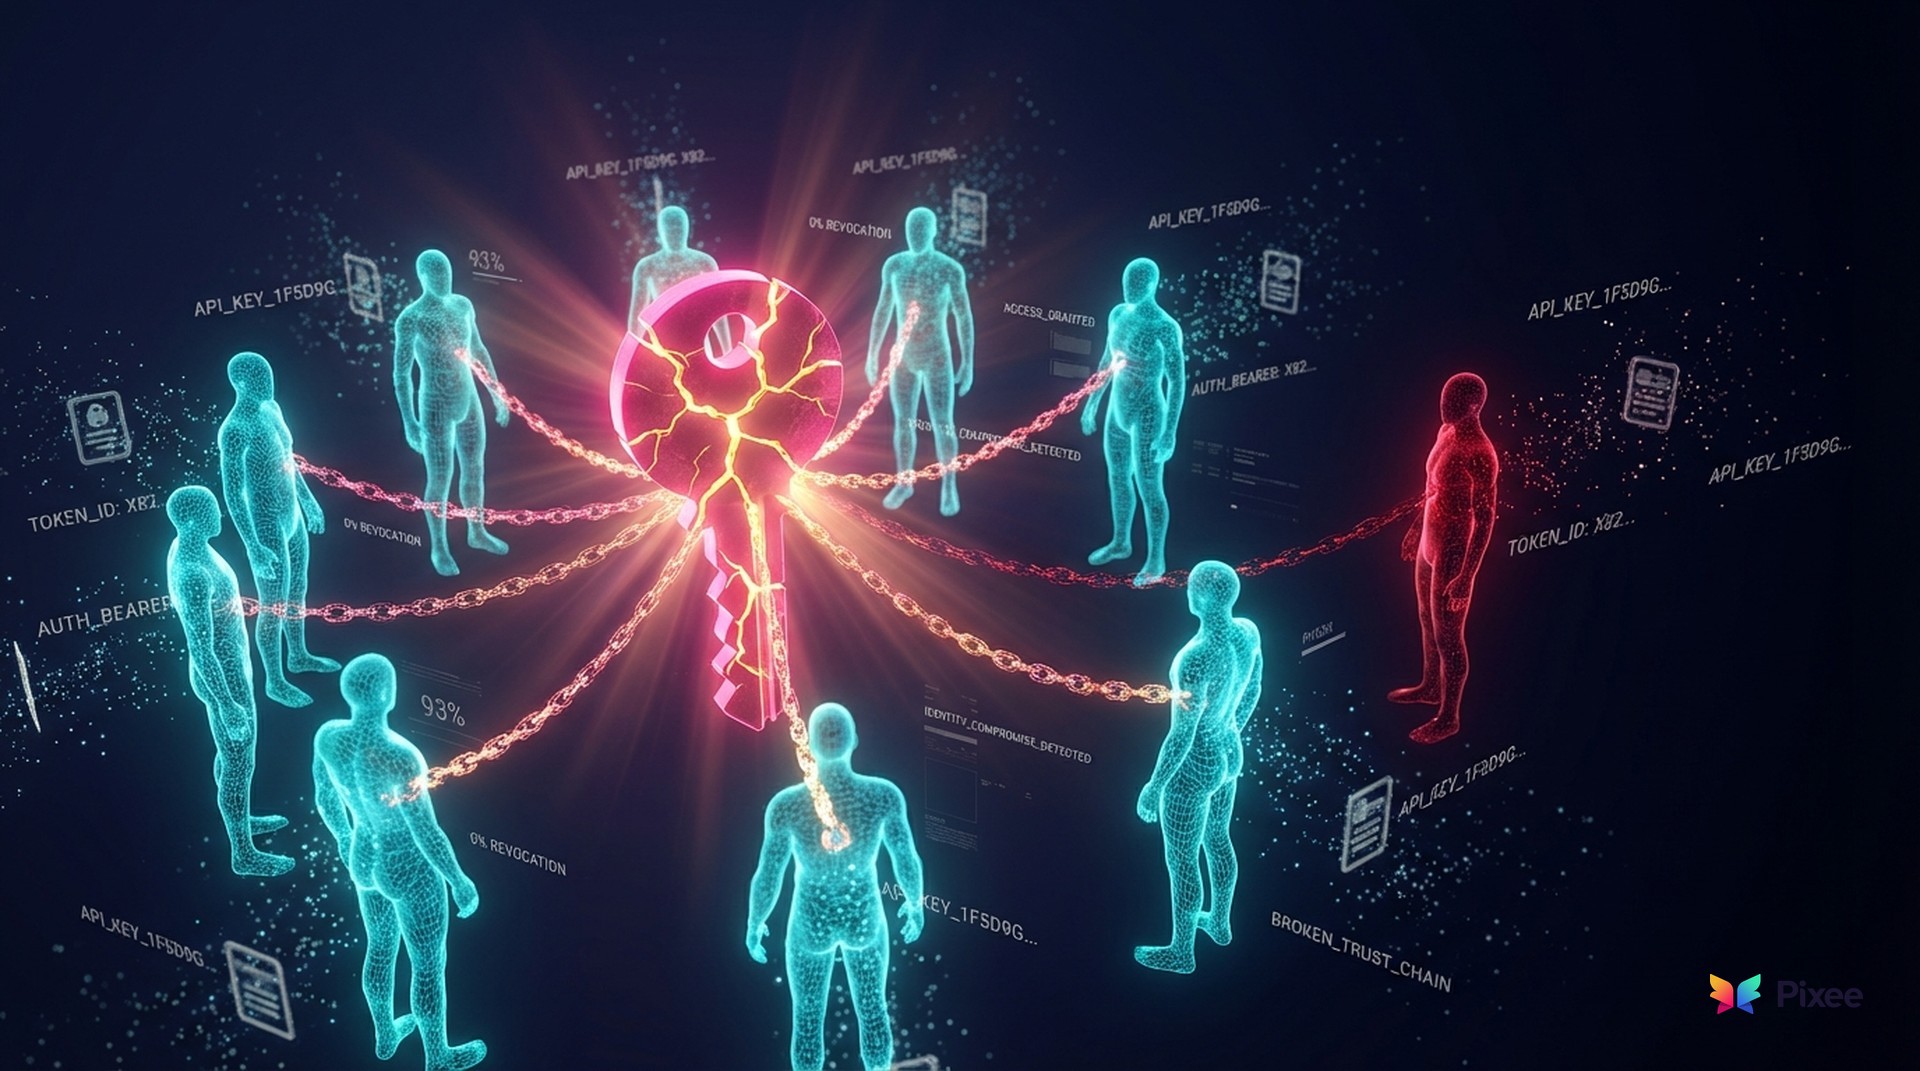
93% of AI Agent Frameworks Have Zero Identity Controls

93% of AI agent frameworks use unscoped API keys. Amazon and Meta suffered production failures from autonomous agents. GlassWorm hit 400+ repos with Solana C2.
Learn More
March 11, 2026

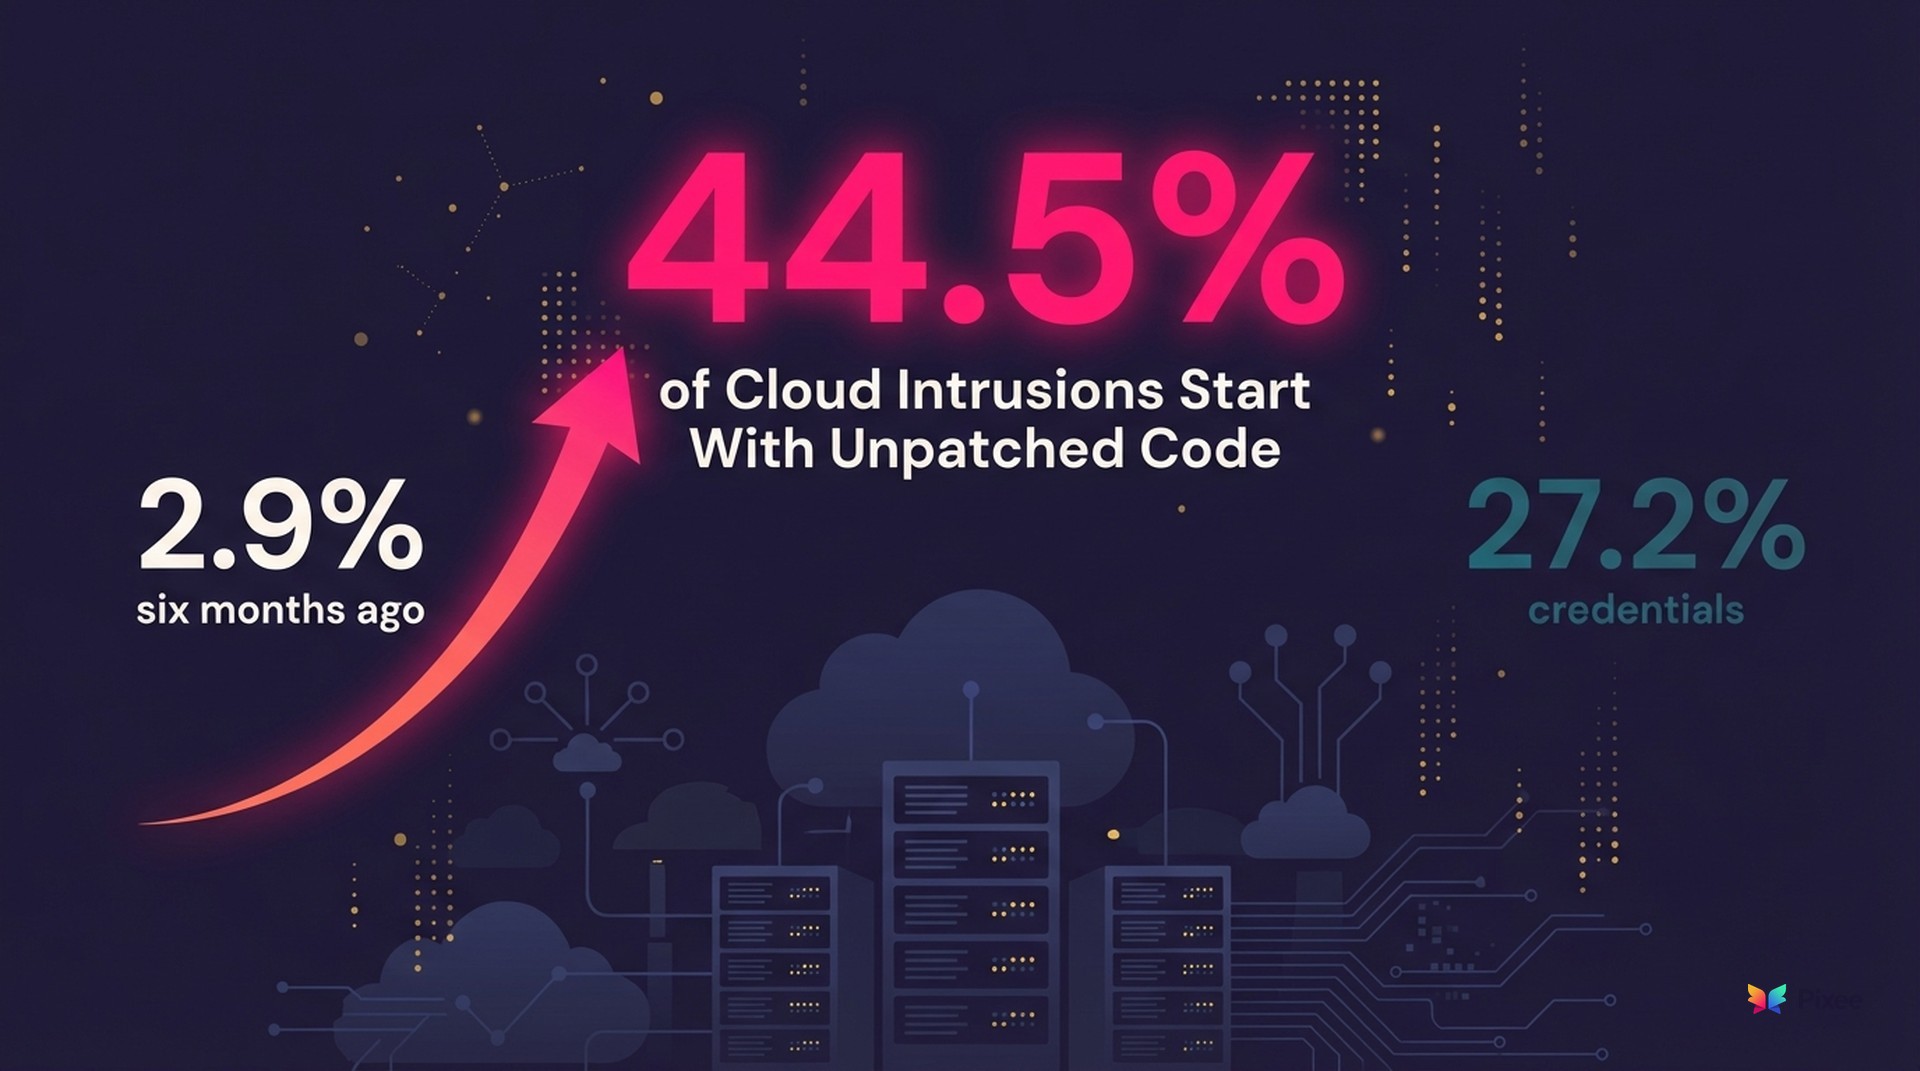
44.5% of Cloud Intrusions Now Start With Unpatched Code

Google Cloud data: software vulns hit 44.5% of cloud intrusions (up from 2.9%), overtaking credentials. APIs are 43% of CISA KEV. OpenAI enters AppSec. $325M bets on agentic security.
Learn More
March 4, 2026

Jailbroken Claude Stole 150GB from a Government

AI coding assistants weaponized in Mexican government breach stealing 150GB. Datadog confirms 87% run exploitable code. Anthropic banned from Pentagon.
Learn More
February 25, 2026

Claude Code Security Spooked Wall Street. The npm Worm Should Have.

Claude Code Security erased billions in market cap over capabilities that already existed. A self-spreading npm worm hit 50,000 downloads targeting AI coding tools. Russian actors used commercial AI to compromise hundreds of firewalls.
Learn More
February 11, 2026

OpenClaw's 180K-Star Marketplace Was 12% Malware

AI agent platforms shipped malware and RCE exploits. Claude found 500+ vulnerabilities. Google closed $32B Wiz deal. Governance can't keep pace.
Learn More
February 4, 2026

69% of C-Suite Execs Use Shadow AI. Your Security Policy Doesn't Apply to Them. | Jan 31-Feb 4

Half of enterprise employees use shadow AI with sensitive data. 69% of C-suite executives prioritize speed over privacy. AI security tools miss what humans catch.
Learn More
January 28, 2026

Claude 4.5 Executed the Equifax Breach in Hours | Jan 23-28

AI pentesting now costs $18/hour. npm says zero-days are your problem. Sonnet 4.5 can exploit breaches without customization.
Learn More
January 21, 2026

AI Coding Tools Systematically Ship Security Flaws Your Scanner Won't Find | Jan 15-21

Tenzai research proves all 5 major AI coding assistants generate critical business logic flaws. Prompt injection hits Google Gemini, Microsoft Copilot, Anthropic MCP. Europe launches GCVE vulnerability database.
Learn More
January 14, 2026

2026 Predictions + Expert Roundup | Jan 9-14

What 30 security leaders learned in 2025 and what they're watching in 2026. Plus EU opens SBOM consultation (Feb 3 deadline) and ZombieAgent compromises ChatGPT via emoji smuggling.
Learn More
January 7, 2026

React2Shell Hit Botnets and supply chain vulns cost $ | Jan 1-7

RondoDox botnet weaponizes React2Shell faster than patching cycles. Trust Wallet's $8.5M theft marks first major supply chain financial attribution. Plus 10K firewalls still vulnerable to 5-year-old CVE.
Learn More
December 31, 2025

MongoBleed Exploited Christmas Morning, 87K Servers at Risk | Dec 25-31

MongoBleed exploited within hours of disclosure. OWASP releases first Agentic AI Top 10. Plus AI coding tools face real-world limitations reality check.
Learn More
December 24, 2025

AI Code Ships With 2.74× More Security Flaws | Dec 19-24

CodeRabbit research: AI-generated code has 2.74× more security issues than human-written. NPM package steals WhatsApp credentials after 56K downloads. Plus $11B in security M&A.
Learn More
December 17, 2025

Five China-Nexus Groups Exploited React2Shell | Dec 13-17

Google documents coordinated nation-state exploitation. UK government says prompt injection can't be fully mitigated. Microsoft expands bug bounties to all third-party code.
Learn More
December 10, 2025

When the Patch Causes an Outage - React2Shell Broke Cloudflare, Shopify, Zoom | Dec 6-10

React2Shell will be fixed because it has visibility, urgency, and buy-in. Your backlog of medium-severity CVEs will not.
Learn More
December 3, 2025

98% of Companies Deploy AI Agents, 79% Have No Security Policy | Nov 27 - Dec 3

98% of enterprises deploy AI agents but 79% have no written security policies. Fragmented tooling creates 4-week MTTR for critical vulnerabilities. AI coding tools becoming attack surfaces. $190M+ funding validates automated remediation.
Learn More
November 26, 2025

npm Worm, CISA Deadlines, and the AI Productivity Question

25,000 npm packages compromised in one week. CISA's December 12 deadline for Oracle Identity Manager. DevOps analysis questions whether AI coding velocity translates to actual productivity.
Learn More
November 19, 2025

Attackers Automated 90% of Operations with Claude AI | Nov 15-19

Chinese state-sponsored actors automated 90% of cyberattack operations using Claude AI while 30,000 EU organizations face December NIS2 compliance deadlines. Seven zero-days under active exploitation demonstrate ongoing response velocity gap.
Learn More
November 12, 2025

50% of CISOs Report Security Burnout. GitHub Copilot Reports First CVE

50% of CISOs report burnout affecting breach preparedness while 80+ critical CVEs landed in one week. Operational capacity hits the wall as teams drown in alerts and patch volumes exceed human triage capacity.
Learn More
November 5, 2025

Aardvark Validates Automated Remediation while AI Tools Expose New Risks

OpenAI's Aardvark validates automated remediation market while AI platforms expose critical security flaws. OWASP conference agenda signals industry shift from detection to remediation focus.
Learn More
October 29, 2025

AI Writes Code Faster Than Security Teams Can Fix It

AI code generation outpaces remediation capacity with 76% of security teams struggling. Five critical CVEs exploited, 3,000+ MCP servers breached.
Learn More
October 17, 2025

Nation-State Attacks Expose the Limits of Reactive Security

Nation-state actors stole F5 source code to build zero-days before patches exist. Adobe AEM exploitation outpaces patch cycles. Weekly intelligence.
Learn More
October 8, 2025

Pre-Patch Exploitation Era Begins

Attackers exploit Oracle zero-days two months before patches exist. AI coding tools accelerate production while security teams struggle with manual triage.
Learn More

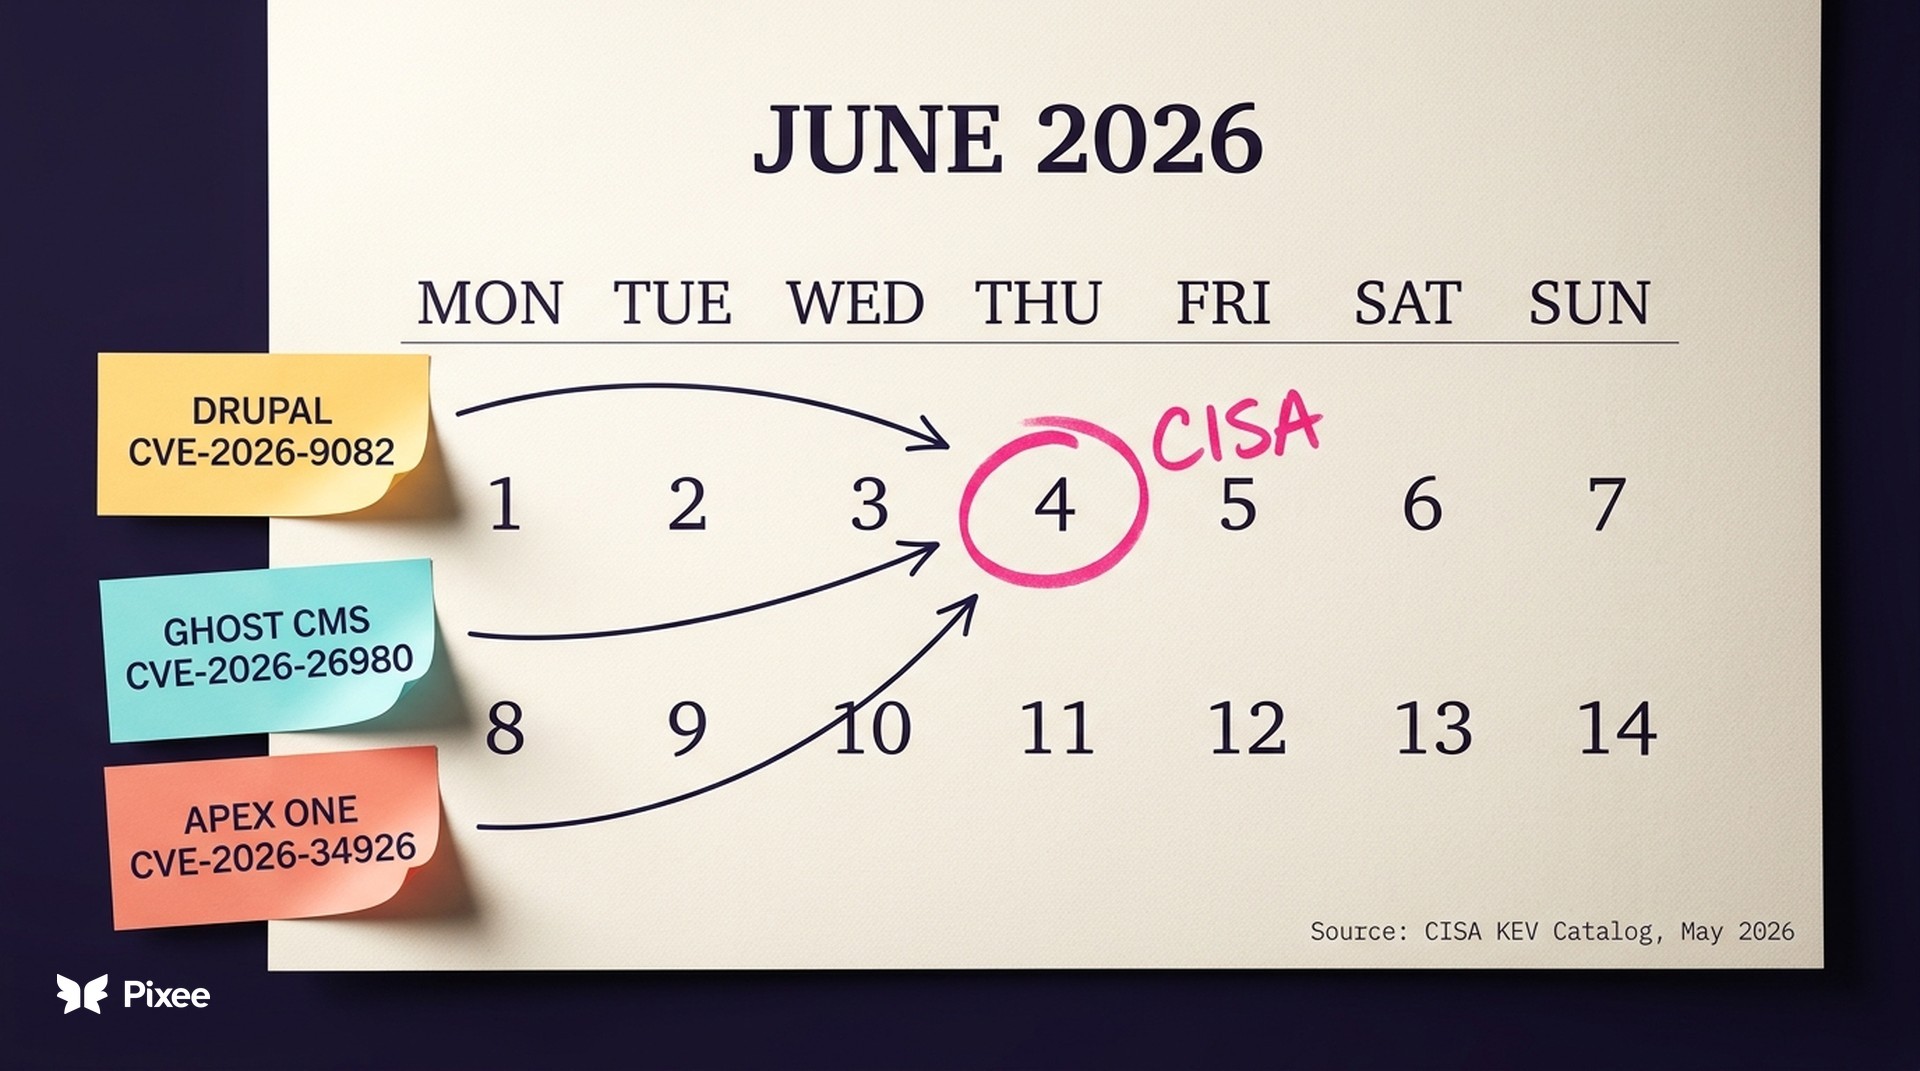
Drupal, Ghost, and Apex One Hit Active Exploitation. Apex One Has a June 4 Federal Deadline.

Drupal, Ghost CMS, and Trend Micro Apex One all entered active exploitation; CISA set a June 4 federal deadline on Apex One.
Learn More
Weekly Intel

AppSec Weekly

The briefing security leaders actually read. CVEs, tooling shifts, and remediation trends — every week in 5 minutes.

Weekly only. No spam. Unsubscribe anytime.